Services
All Services
Audit
Business
Cybersecurity
Compliance
Privacy
Technology
Thank you! Your submission has been received!
Oops! Something went wrong while submitting the form.
Agentforce Consulting
TECHNOLOGY
Agentic AI Security
CYBERSECURITY
AI-Augmented Offensive Security
CYBERSECURITY
AI Governance Consulting
PRIVACY
AI Implementation
TECHNOLOGY
AI Integration
TECHNOLOGY
AI Readiness Assessment
TECHNOLOGY
AI Strategy Consulting
TECHNOLOGY
API Penetration Testing
CYBERSECURITY
Application Modernization
TECHNOLOGY
AuditBoard Consulting
CYBERSECURITY
Audit Services
AUDIT
Automation Consulting
TECHNOLOGY
Banking Software Development
TECHNOLOGY
Build vs Buy Software
TECHNOLOGY
Buy-Side M&A Advisory
Business
Carve-Out Advisory
Business
Carve-Out Cybersecurity
Business
Change Management Consulting
Business
Claims Management Software
TECHNOLOGY
Cloud Migration
TECHNOLOGY
Cloud Security Assessment
CYBERSECURITY
CMMC Compliance Consulting
Compliance
CMMC Gap Assessment
Compliance
Commercial Due Diligence
Business
Consent Management
PRIVACY
Continuous Penetration Testing
CYBERSECURITY
Cultural Integration Consulting
Business
Custom Software Development
TECHNOLOGY
Cyber Due Diligence
Business
Cyber Incident Response
CYBERSECURITY
Cyber Resilience Act Compliance
Compliance
Cybersecurity Compliance
CYBERSECURITY
Cybersecurity Consulting
CYBERSECURITY
Cybersecurity for Small Business
CYBERSECURITY
Cybersecurity Management
CYBERSECURITY
Cybersecurity Transformation
CYBERSECURITY
Databricks Consulting
TECHNOLOGY
Data Engineering
TECHNOLOGY
Data Privacy Consulting
PRIVACY
Data Strategy
TECHNOLOGY
DevOps & DevSecOps Consulting
CYBERSECURITY
Digital Forensics
CYBERSECURITY
Digital Transformation
TECHNOLOGY
Divestiture Consulting
Business
DPO as a Service
PRIVACY
Drata Implementation
CYBERSECURITY
Enterprise AI Consulting
TECHNOLOGY
ESPR Compliance
Compliance
EU AI Act Consulting
PRIVACY
Executive Consulting
CYBERSECURITY
FedRAMP 20x Readiness
Compliance
FedRAMP Compliance Consulting
Compliance
FedRAMP Penetration Testing & Red Team
CYBERSECURITY
Financial Due Diligence
Business
Fintech Software Development
TECHNOLOGY
Fractional CTO
TECHNOLOGY
GDPR Audit
AUDIT
GDPR Compliance Consulting
Compliance
Generative AI Consulting
TECHNOLOGY
GLBA Compliance Consulting
Compliance
GLBA Internal Audit
AUDIT
GRC Consulting
Compliance
Guidewire Replacement
TECHNOLOGY
Healthcare AI Governance
Compliance
Healthcare Growth Strategy
Business
HIPAA Audit
AUDIT
HIPAA Compliance Consulting
Compliance
HITRUST Consulting
Compliance
Insurance Core Platform
TECHNOLOGY
Insurance Software Development
TECHNOLOGY
Intangible Asset Valuation
Business
Internal Audit Services
AUDIT
Investor Relations Services
Business
IR Retainer
CYBERSECURITY
ISO 27001 Compliance Consulting
Compliance
ISO 27001 Internal Audit
AUDIT
ISO 42001 Compliance Consulting
Compliance
ISO 42001 Internal Audit
AUDIT
IT Carve-Out Services
Business
IT Consulting
TECHNOLOGY
IT Cost Optimization
TECHNOLOGY
M&A Advisory
Business
M&A Advisory Services
Transaction Advisory
M&A Change Management
Business
M&A Clean Room
Business
M&A Due Diligence
Business
Managed Cloud Security
TECHNOLOGY
Managed IT Support
TECHNOLOGY
M&A Tax Due Diligence
Business
Microsoft 365 Security Assessment
CYBERSECURITY
Microsoft Copilot Consulting
TECHNOLOGY
Network Penetration Testing
CYBERSECURITY
Network Security Monitoring
CYBERSECURITY
NIST Compliance Consulting
Compliance
Operational Due Diligence
Business
Palantir AIP & Forward Deployed Engineering
TECHNOLOGY
Palantir Consulting
TECHNOLOGY
Palantir Foundry Implementation
TECHNOLOGY
Palantir Managed Services
TECHNOLOGY
Industries
All Industries
Education
Energy
Financial Services
Government
Healthcare
Legal (Law Firms)
Manufacturing
Marketing Agencies
Retail
Software Development
Startups
Technology
Cases
About
Blog
Book a Call
+1 (804) 913-3012
info@bdemerson.com
linkedin
Thank you! Your submission has been received!
Oops! Something went wrong while submitting the form.
45
results found for your request
Services
Insurance Core Platform
Palantir Managed Services
Transcend Implementation
Cyber Resilience Act Compliance
IT Cost Optimization
Healthcare AI Governance
M&A Clean Room
Digital Forensics
Carve-Out Cybersecurity
IT Carve-Out Services
Divestiture Consulting
Custom Software Development
ESPR Compliance
Guidewire Replacement
FedRAMP 20x Readiness
Intangible Asset Valuation
Healthcare Growth Strategy
SOC 1 Audit
SOX ITGC Audit
GLBA Internal Audit
ISO 42001 Internal Audit
Internal Audit Services
Regulatory Audits
HITRUST Consulting
GRC Consulting
Cultural Integration Consulting
SOX Compliance Consulting
PCI DSS Compliance Consulting
M&A Change Management
Change Management Consulting
Claims Management Software
Policy Administration System
Banking Software Development
Snowflake Consulting
Insurance Software Development
Fintech Software Development
Build vs Buy Software
Post-Merger Integration
Operational Due Diligence
Commercial Due Diligence
M&A Due Diligence
TSA Advisory
Carve-Out Advisory
Quality of Earnings
Cyber Due Diligence
Consent Management
Salesforce Implementation
Cloud Migration
AuditBoard Consulting
Drata Implementation
Agentforce Consulting
Automation Consulting
Microsoft 365 Security Assessment
DevOps & DevSecOps Consulting
ServiceNow GRC Implementation
SOC as a Service
AI Implementation
Application Modernization
Cloud Security Assessment
Tabletop Exercises
IR Retainer
Data Strategy
AI Integration
Generative AI Consulting
System Integration
Microsoft Copilot Consulting
Data Engineering
Agentic AI Security
AI Strategy Consulting
AI Readiness Assessment
Penetration Testing
DPO as a Service
CMMC Gap Assessment
Software & IT Due Diligence
ISO 27001 Internal Audit
Vulnerability Management
API Penetration Testing
Network Penetration Testing
AI-Augmented Offensive Security
Continuous Penetration Testing
FedRAMP Penetration Testing & Red Team
Red Teaming & Offensive Security
Technology & AI for Portfolio Companies
Private Equity Value Creation
Private Equity Consulting
Private LLM Hosting
Databricks Consulting
Enterprise AI Consulting
M&A Advisory Services
Palantir AIP & Forward Deployed Engineering
Palantir Foundry Implementation
Palantir Consulting
Transaction Valuation
M&A Tax Due Diligence
Financial Due Diligence
Sell-Side M&A Advisory
Buy-Side M&A Advisory
M&A Advisory
Transaction Advisory
Investor Relations Services
Industries
Healthcare
Financial Services
Retail
Education
Technology
Manufacturing
Government
Energy
Legal (Law Firms)
Software Development
Marketing Agencies
Startups
Cases
B2B Software Company
Boxcore
Captive Auto Finance Company
Civex
Consumer Technology Company
Data and Analytics Company
Dedupely
DeepOpinion
Defense Software Company
Dental Laboratory Group
Enterprise SaaS Provider
FGI Worldwide
Gardiant
Give Interactive
Global Reinsurer
Gordon Brothers
GovCon Software Provider
HiredHelpr
Incentiv
Industrial Manufacturer
Intellinum
Investment Firm
Life and Annuity Insurer
Life Insurance Carrier
LifeLenz
Lincoln Industries
LiveSchool
Major Energy Company
Major Fintech Business
Major Hospital System
Major Insurance Provider
mdhub
Meridian AI
Murtha Cullina
OpenEvidence
PE-Backed Healthcare Platform
Rubrik
Savant/GE Lighting
Semiconductor Company
Spare
Supered
Tag1
TalentNeuron
Thomson Reuters Special Services
Titan Intake
Wendt Partners
Articles
Application Rationalization: How to Shrink the Portfolio Before You Modernize It
Insurance Rating Software: How a Carrier Rating Engine Works and How to Choose One
Palantir Foundry Dashboards: Contour, Quiver, Workshop, and Which Tool to Use
Threat Hunting: How a Hunt Program Works and When to Build or Buy One
Data Migration Strategy: Cutover Options, Reconciliation, and How Much History to Move
Insurity: Products, Ownership, and How It Compares With Other P&C Core Vendors
Buy and Build Strategy: How Private Equity Platforms Grow Through Add-On Acquisitions
Palantir Certifications: What Each One Proves and Which Your Platform Team Needs
Detection Engineering: How to Build the Function Behind Your SOC's Alerts
Veterinary Private Equity: How Vet Practice Deals Work and What Buyers Must Diligence
How to Start an Insurance Company: Capital, Licensing, and the Systems to Run It
Cloud Migration Strategy: The 7 Rs, the Wave Plan, and the Business Case
Palantir MCP and Ontology MCP: How AI Agents Build On and Act Through Foundry
Customer Concentration Risk: How Buyers Measure It, Price It, and Protect Against It
SIEM vs SOAR: What Each Does, and When You Need a Separate SOAR
Insurance Billing Software for P&C Carriers and MGAs: What It Must Do
Material Adverse Effect (MAE) Clauses: What Delaware Courts Require and What the Numbers Must Show
Mainframe Modernization: Five Paths, the Cost Math, and Why Programs Run Long
Palantir FDE Handoff: What to Have in Hand Before the Forward Deployed Engineers Leave
SOC Automation: What to Automate First, and What Stays Human
Dental Practice Acquisition: The Due Diligence That Protects the Deal
Incident Response Plan Template: What Each Section Must Say
Rollover Equity: How Sellers Keep a Stake in a Private Equity Deal
AI Acceptable Use Policy: What It Must Cover
SIEM as a Service: Scope, Pricing, and When It Fits
What Is a C3PAO? How CMMC Third-Party Assessments Work
OneTrust vs Transcend: How They Differ and What Switching Takes
Vendor Risk Assessment: How to Tier, Review, and Decide
Scalable Third-Party Risk Management for SaaS Companies
Transition Services Agreement Benchmark: Terms From 39 SEC-Filed Separations, 2020 to 2026
IEC 62443 Explained: Parts, Security Levels, and Certification
SBOM Requirements: CRA, FDA, Federal Contracts, and PCI DSS
CRA Reporting Obligations: Article 14 Deadlines and Process
Cyber Resilience Act: What the EU CRA Requires and When
Cloud Cost Optimization: The Levers That Pay Back First
Software License Optimization: Cut Publisher Costs and Prepare for Audits
SaaS Spend Management: Find Every App and Cut Waste Before Renewal
AI in Revenue Cycle Management: Uses, Risks, and Controls
HIPAA and AI: How HIPAA Applies to Building, Buying, and Using AI
Is ChatGPT HIPAA Compliant? Which Plans Come With a BAA
M&A Day 1 Readiness Checklist: What Has to Work the Morning After Close
Private Equity Carve-Outs: Returns, Diligence, and the Path to Standalone
Cybersecurity Expert Witness: Consulting and Testifying Roles
Litigation Hold: When the Duty Starts and How to Preserve Each System
Kovel Agreement: When a Breach Forensic Report Stays Privileged
Employee Data Theft: How to Investigate a Departing Employee
Ransomware Investigation: What to Establish in the First Week
Cyber Forensics: What It Proves and How an Investigation Runs
363 Sale: How to Buy a Company Out of Bankruptcy
Clean Team Agreement: How Merging Competitors Avoid Gun Jumping
Cybersecurity Due Diligence Checklist: 10 Areas to Review in M&A
AI Agent Permissions: How to Limit What an Agent Can Actually Do
Vanta vs. ServiceNow GRC: What Changes as You Scale?
Growth Equity: How It Works and How It Differs From Venture Capital and Buyouts
Net Working Capital in M&A: Formula, Peg, and True-Up
Vulnerability Assessment vs Penetration Testing: What Each Finds and When You Need It
MVP Development: Scope, Cost, Timeline, and Process
Staff Augmentation: How It Works, What It Costs, and When to Use It
Cyber Kill Chain: The Seven Stages and How Defenders Use Them
MITRE ATT&CK Framework: Tactics, Techniques, and How Teams Use It
Confidential Information Memorandum (CIM): What It Contains and How Buyers Read It
Software Development Outsourcing: Models, Costs, and Vendor Selection
Representations and Warranties Insurance: Cost, Coverage, and Claims
Maven Smart System: What Palantir's Military AI Platform Does
Black Box vs White Box vs Gray Box Penetration Testing
Policy Administration System: What It Does and How to Choose One
Majesco: Products, Ownership, and How It Compares With Guidewire
Asset Sale vs Stock Sale: Tax, Liability, and Deal Structure
Data Governance Framework: Components, Models, and a 90-Day Plan
HIPAA Compliance Checklist: Privacy, Security, and Breach Rules
Business Continuity vs Disaster Recovery: Differences, Plans, and Testing
Medallion Architecture: Bronze, Silver, and Gold Layers Explained
Business Impact Analysis (BIA): Method, Template, and Example
HIPAA Security Risk Assessment: How to Conduct a Risk Analysis
What Is PCI Compliance? Merchant Levels, SAQ Types, and QSAs
What Is Shadow AI? Risks, Detection, and an AI Acceptable Use Policy
HITRUST Certification: e1, i1, and r2 Assessments, Cost, and Timeline
PCI Compliance Cost: Ranges by Level, SAQ, and ROC
Best Data Governance Tools in 2026: 10 Platforms Ranked
What Is a SOC 1 Report? SSAE 18, Type 1, and Type 2 Explained
DSAR: How to Handle a Data Subject Access Request
What Is the Model Context Protocol (MCP)? An Enterprise Guide
SOC 1 vs SOC 2 vs SOC 3: Differences and Which You Need
Duck Creek Technologies: Products, Platform, and Guidewire Comparison
What Is an Earn Out? How Earnouts Work in M&A
Types of Mergers: Horizontal, Vertical, Conglomerate, and More
Insurance Claims Management System: A P&C Buyer's Guide
Internal vs External Penetration Testing
Private Equity Due Diligence: Workstreams, Timeline, and Checklist
Custom AI Development: Architectures, Costs, and the Path to Production
What Is AI Red Teaming? Methods, Frameworks, and Tools
What Does Palantir Do? Products, Customers, and Business Model
Red Team vs Blue Team vs Purple Team
Best Custom Software Development Companies in 2026: A Ranked Shortlist for Regulated Enterprises
What Is Red Teaming? How Red Team Assessments Work
Palantir Gotham: What It Is, Who Uses It, and How It Differs From Foundry
Custom Software Development Cost in 2026: Ranges, Rates, and a Worked Example
When Is a DPIA Required? Data Protection Impact Assessments and US State Rules
Cybersecurity Budgets Planning Guide: How to Build, Break Down, and Defend a Cybersecurity Budget
Digital Product Passport: What It Is and What the EU Requires
Oops!
Please try entering your query differently.
Book a Call
Services
Back
All Services
SOC 2 Compliance Consulting
ISO 27001 Compliance Consulting
CMMC Compliance Consulting
FedRAMP Compliance Consulting
Data Privacy Consulting
Penetration Testing
SOC as a Service
IR Retainer
vCISO Services
Enterprise AI Consulting
AI Implementation
Palantir Consulting
Databricks Consulting
Digital Transformation
M&A Advisory
Industries
Back
All Industries
Marketing Agencies
Startups
Software Development
Energy
Legal (Law Firms)
Government
Manufacturing
Healthcare
Financial Services
Technology
Education
Retail
Cases
About
Blog
Book a Call
+1 (804) 913-3012
info@bdemerson.com
linkedin
Thank you! Your submission has been received!
Oops! Something went wrong while submitting the form.
45
results found for your request
Services
Insurance Core Platform
Palantir Managed Services
Transcend Implementation
Cyber Resilience Act Compliance
IT Cost Optimization
Healthcare AI Governance
M&A Clean Room
Digital Forensics
Carve-Out Cybersecurity
IT Carve-Out Services
Divestiture Consulting
Custom Software Development
ESPR Compliance
Guidewire Replacement
FedRAMP 20x Readiness
Intangible Asset Valuation
Healthcare Growth Strategy
SOC 1 Audit
SOX ITGC Audit
GLBA Internal Audit
ISO 42001 Internal Audit
Internal Audit Services
Regulatory Audits
HITRUST Consulting
GRC Consulting
Cultural Integration Consulting
SOX Compliance Consulting
PCI DSS Compliance Consulting
M&A Change Management
Change Management Consulting
Claims Management Software
Policy Administration System
Banking Software Development
Snowflake Consulting
Insurance Software Development
Fintech Software Development
Build vs Buy Software
Post-Merger Integration
Operational Due Diligence
Commercial Due Diligence
M&A Due Diligence
TSA Advisory
Carve-Out Advisory
Quality of Earnings
Cyber Due Diligence
Consent Management
Salesforce Implementation
Cloud Migration
AuditBoard Consulting
Drata Implementation
Agentforce Consulting
Automation Consulting
Microsoft 365 Security Assessment
DevOps & DevSecOps Consulting
ServiceNow GRC Implementation
SOC as a Service
AI Implementation
Application Modernization
Cloud Security Assessment
Tabletop Exercises
IR Retainer
Data Strategy
AI Integration
Generative AI Consulting
System Integration
Microsoft Copilot Consulting
Data Engineering
Agentic AI Security
AI Strategy Consulting
AI Readiness Assessment
Penetration Testing
DPO as a Service
CMMC Gap Assessment
Software & IT Due Diligence
ISO 27001 Internal Audit
Vulnerability Management
API Penetration Testing
Network Penetration Testing
AI-Augmented Offensive Security
Continuous Penetration Testing
FedRAMP Penetration Testing & Red Team
Red Teaming & Offensive Security
Technology & AI for Portfolio Companies
Private Equity Value Creation
Private Equity Consulting
Private LLM Hosting
Databricks Consulting
Enterprise AI Consulting
M&A Advisory Services
Palantir AIP & Forward Deployed Engineering
Palantir Foundry Implementation
Palantir Consulting
Transaction Valuation
M&A Tax Due Diligence
Financial Due Diligence
Sell-Side M&A Advisory
Buy-Side M&A Advisory
M&A Advisory
Transaction Advisory
Investor Relations Services
Industries
Healthcare
Financial Services
Retail
Education
Technology
Manufacturing
Government
Energy
Legal (Law Firms)
Software Development
Marketing Agencies
Startups
Cases
B2B Software Company
Boxcore
Captive Auto Finance Company
Civex
Consumer Technology Company
Data and Analytics Company
Dedupely
DeepOpinion
Defense Software Company
Dental Laboratory Group
Enterprise SaaS Provider
FGI Worldwide
Gardiant
Give Interactive
Global Reinsurer
Gordon Brothers
GovCon Software Provider
HiredHelpr
Incentiv
Industrial Manufacturer
Intellinum
Investment Firm
Life and Annuity Insurer
Life Insurance Carrier
LifeLenz
Lincoln Industries
LiveSchool
Major Energy Company
Major Fintech Business
Major Hospital System
Major Insurance Provider
mdhub
Meridian AI
Murtha Cullina
OpenEvidence
PE-Backed Healthcare Platform
Rubrik
Savant/GE Lighting
Semiconductor Company
Spare
Supered
Tag1
TalentNeuron
Thomson Reuters Special Services
Titan Intake
Wendt Partners
Articles
Application Rationalization: How to Shrink the Portfolio Before You Modernize It
Insurance Rating Software: How a Carrier Rating Engine Works and How to Choose One
Palantir Foundry Dashboards: Contour, Quiver, Workshop, and Which Tool to Use
Threat Hunting: How a Hunt Program Works and When to Build or Buy One
Data Migration Strategy: Cutover Options, Reconciliation, and How Much History to Move
Insurity: Products, Ownership, and How It Compares With Other P&C Core Vendors
Buy and Build Strategy: How Private Equity Platforms Grow Through Add-On Acquisitions
Palantir Certifications: What Each One Proves and Which Your Platform Team Needs
Detection Engineering: How to Build the Function Behind Your SOC's Alerts
Veterinary Private Equity: How Vet Practice Deals Work and What Buyers Must Diligence
How to Start an Insurance Company: Capital, Licensing, and the Systems to Run It
Cloud Migration Strategy: The 7 Rs, the Wave Plan, and the Business Case
Palantir MCP and Ontology MCP: How AI Agents Build On and Act Through Foundry
Customer Concentration Risk: How Buyers Measure It, Price It, and Protect Against It
SIEM vs SOAR: What Each Does, and When You Need a Separate SOAR
Insurance Billing Software for P&C Carriers and MGAs: What It Must Do
Material Adverse Effect (MAE) Clauses: What Delaware Courts Require and What the Numbers Must Show
Mainframe Modernization: Five Paths, the Cost Math, and Why Programs Run Long
Palantir FDE Handoff: What to Have in Hand Before the Forward Deployed Engineers Leave
SOC Automation: What to Automate First, and What Stays Human
Dental Practice Acquisition: The Due Diligence That Protects the Deal
Incident Response Plan Template: What Each Section Must Say
Rollover Equity: How Sellers Keep a Stake in a Private Equity Deal
AI Acceptable Use Policy: What It Must Cover
SIEM as a Service: Scope, Pricing, and When It Fits
What Is a C3PAO? How CMMC Third-Party Assessments Work
OneTrust vs Transcend: How They Differ and What Switching Takes
Vendor Risk Assessment: How to Tier, Review, and Decide
Scalable Third-Party Risk Management for SaaS Companies
Transition Services Agreement Benchmark: Terms From 39 SEC-Filed Separations, 2020 to 2026
IEC 62443 Explained: Parts, Security Levels, and Certification
SBOM Requirements: CRA, FDA, Federal Contracts, and PCI DSS
CRA Reporting Obligations: Article 14 Deadlines and Process
Cyber Resilience Act: What the EU CRA Requires and When
Cloud Cost Optimization: The Levers That Pay Back First
Software License Optimization: Cut Publisher Costs and Prepare for Audits
SaaS Spend Management: Find Every App and Cut Waste Before Renewal
AI in Revenue Cycle Management: Uses, Risks, and Controls
HIPAA and AI: How HIPAA Applies to Building, Buying, and Using AI
Is ChatGPT HIPAA Compliant? Which Plans Come With a BAA
M&A Day 1 Readiness Checklist: What Has to Work the Morning After Close
Private Equity Carve-Outs: Returns, Diligence, and the Path to Standalone
Cybersecurity Expert Witness: Consulting and Testifying Roles
Litigation Hold: When the Duty Starts and How to Preserve Each System
Kovel Agreement: When a Breach Forensic Report Stays Privileged
Employee Data Theft: How to Investigate a Departing Employee
Ransomware Investigation: What to Establish in the First Week
Cyber Forensics: What It Proves and How an Investigation Runs
363 Sale: How to Buy a Company Out of Bankruptcy
Clean Team Agreement: How Merging Competitors Avoid Gun Jumping
Cybersecurity Due Diligence Checklist: 10 Areas to Review in M&A
AI Agent Permissions: How to Limit What an Agent Can Actually Do
Vanta vs. ServiceNow GRC: What Changes as You Scale?
Growth Equity: How It Works and How It Differs From Venture Capital and Buyouts
Net Working Capital in M&A: Formula, Peg, and True-Up
Vulnerability Assessment vs Penetration Testing: What Each Finds and When You Need It
MVP Development: Scope, Cost, Timeline, and Process
Staff Augmentation: How It Works, What It Costs, and When to Use It
Cyber Kill Chain: The Seven Stages and How Defenders Use Them
MITRE ATT&CK Framework: Tactics, Techniques, and How Teams Use It
Confidential Information Memorandum (CIM): What It Contains and How Buyers Read It
Software Development Outsourcing: Models, Costs, and Vendor Selection
Representations and Warranties Insurance: Cost, Coverage, and Claims
Maven Smart System: What Palantir's Military AI Platform Does
Black Box vs White Box vs Gray Box Penetration Testing
Policy Administration System: What It Does and How to Choose One
Majesco: Products, Ownership, and How It Compares With Guidewire
Asset Sale vs Stock Sale: Tax, Liability, and Deal Structure
Data Governance Framework: Components, Models, and a 90-Day Plan
HIPAA Compliance Checklist: Privacy, Security, and Breach Rules
Business Continuity vs Disaster Recovery: Differences, Plans, and Testing
Medallion Architecture: Bronze, Silver, and Gold Layers Explained
Business Impact Analysis (BIA): Method, Template, and Example
HIPAA Security Risk Assessment: How to Conduct a Risk Analysis
What Is PCI Compliance? Merchant Levels, SAQ Types, and QSAs
What Is Shadow AI? Risks, Detection, and an AI Acceptable Use Policy
HITRUST Certification: e1, i1, and r2 Assessments, Cost, and Timeline
PCI Compliance Cost: Ranges by Level, SAQ, and ROC
Best Data Governance Tools in 2026: 10 Platforms Ranked
What Is a SOC 1 Report? SSAE 18, Type 1, and Type 2 Explained
DSAR: How to Handle a Data Subject Access Request
What Is the Model Context Protocol (MCP)? An Enterprise Guide
SOC 1 vs SOC 2 vs SOC 3: Differences and Which You Need
Duck Creek Technologies: Products, Platform, and Guidewire Comparison
What Is an Earn Out? How Earnouts Work in M&A
Types of Mergers: Horizontal, Vertical, Conglomerate, and More
Insurance Claims Management System: A P&C Buyer's Guide
Internal vs External Penetration Testing
Private Equity Due Diligence: Workstreams, Timeline, and Checklist
Custom AI Development: Architectures, Costs, and the Path to Production
What Is AI Red Teaming? Methods, Frameworks, and Tools
What Does Palantir Do? Products, Customers, and Business Model
Red Team vs Blue Team vs Purple Team
Best Custom Software Development Companies in 2026: A Ranked Shortlist for Regulated Enterprises
What Is Red Teaming? How Red Team Assessments Work
Palantir Gotham: What It Is, Who Uses It, and How It Differs From Foundry
Custom Software Development Cost in 2026: Ranges, Rates, and a Worked Example
When Is a DPIA Required? Data Protection Impact Assessments and US State Rules
Cybersecurity Budgets Planning Guide: How to Build, Break Down, and Defend a Cybersecurity Budget
Digital Product Passport: What It Is and What the EU Requires
Oops!
Please try entering your query differently.
Home
/
Blog
Blog
Insights on strategy, transactions, technology, security, and compliance from BD Emerson's practitioners.
Get a Quote
Compliance
/
July 13, 2026
How to Build a Data Privacy Compliance Program: Everything You Need to Know
Read
Blog
All articles
Dive into our collection of news on the latest privacy laws, security standards, and lessons learned from breaches
Technology
/
November 7, 2026
AI Acceptable Use Policy: What It Must Cover
Read
M&A
/
November 7, 2026
Rollover Equity: How Sellers Keep a Stake in a Private Equity Deal
Read
Cybersecurity
/
November 7, 2026
Incident Response Plan Template: What Each Section Must Say
Read
M&A
/
November 7, 2026
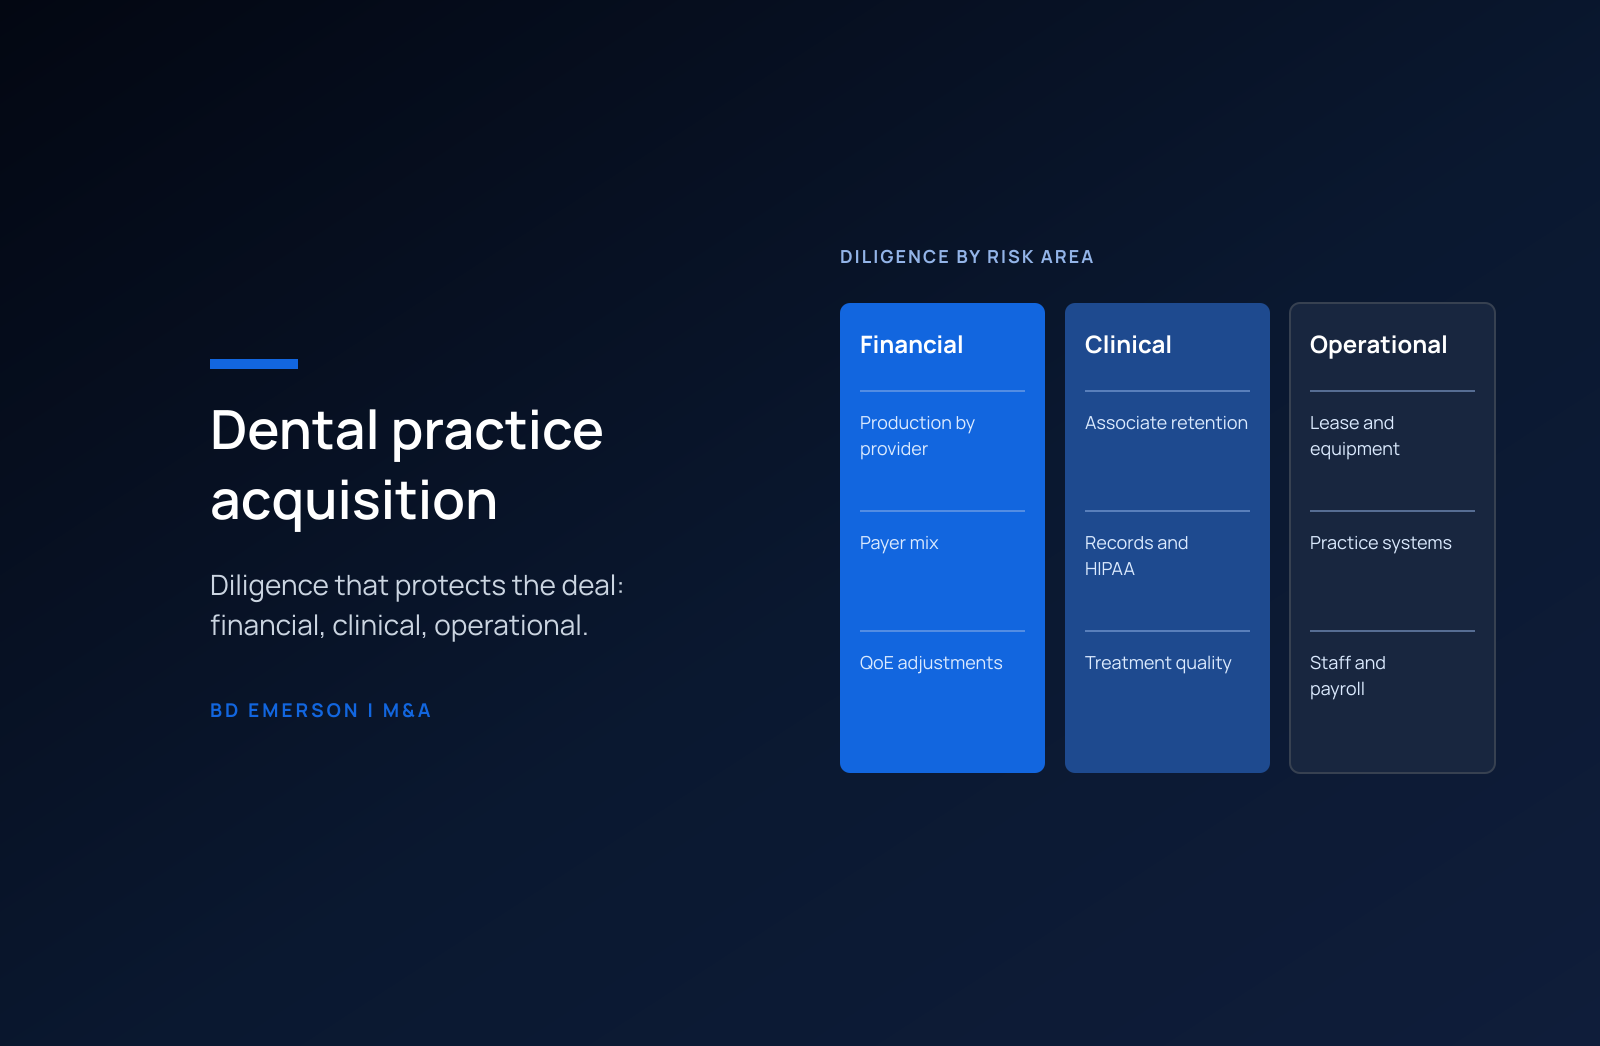
Dental Practice Acquisition: The Due Diligence That Protects the Deal
Read
Cybersecurity
/
November 7, 2026
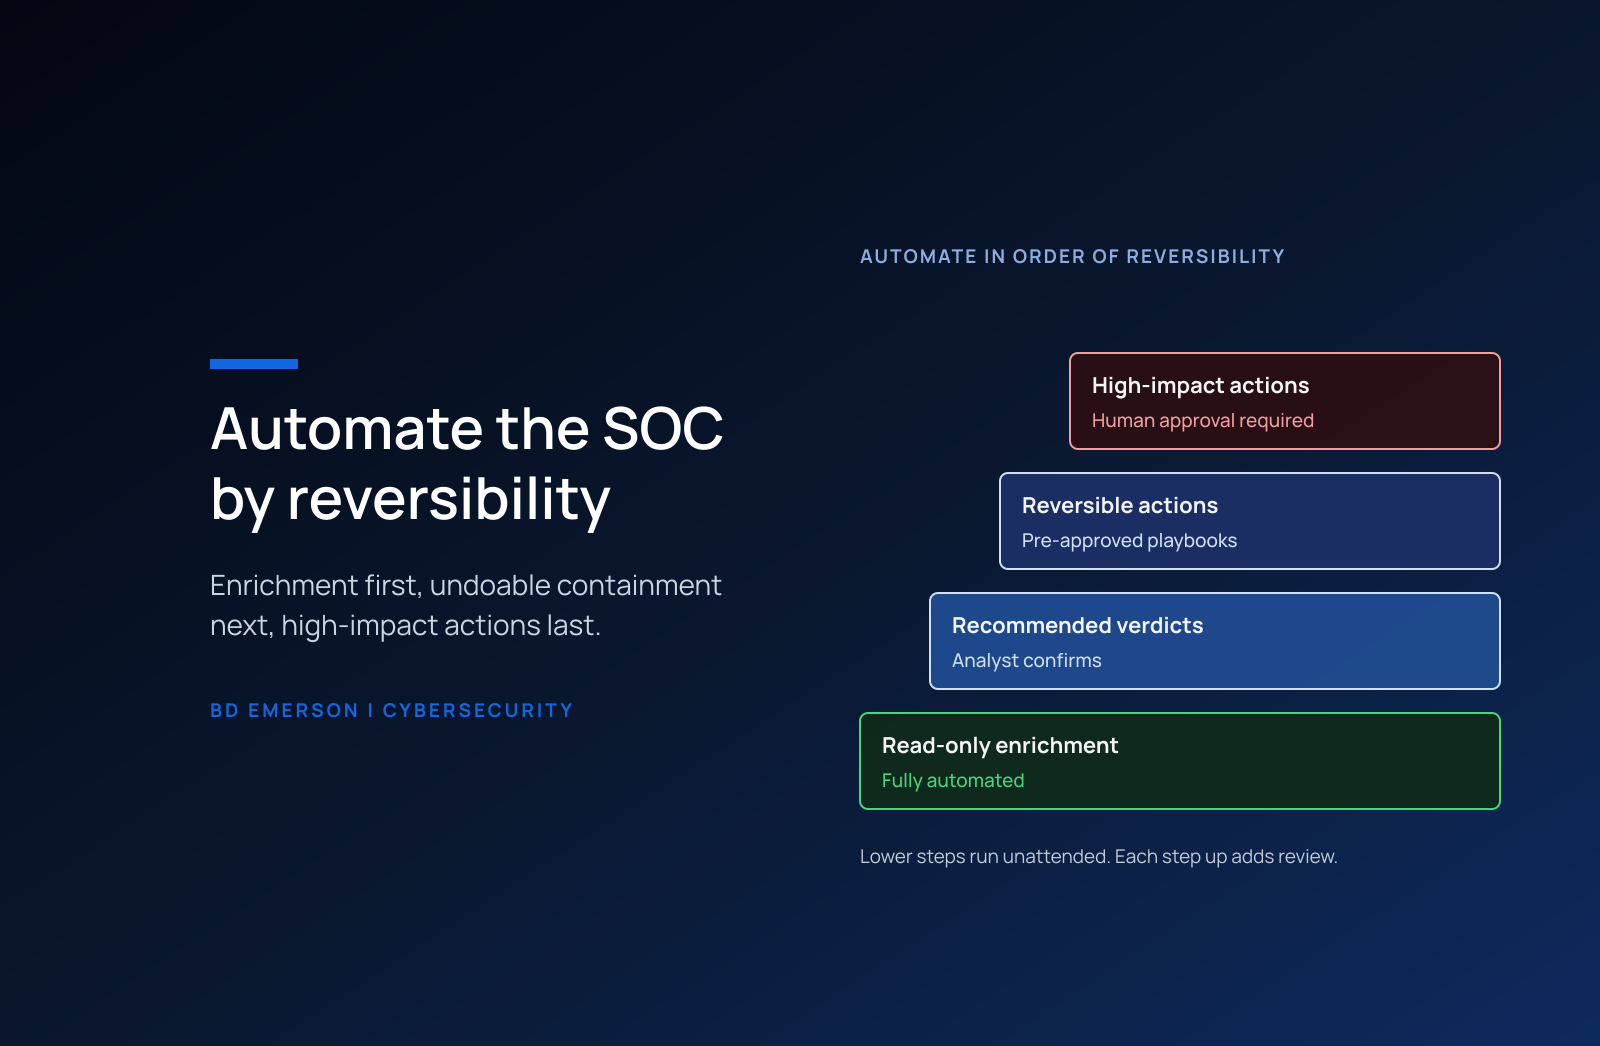
SOC Automation: What to Automate First, and What Stays Human
Read
Technology
/
November 7, 2026
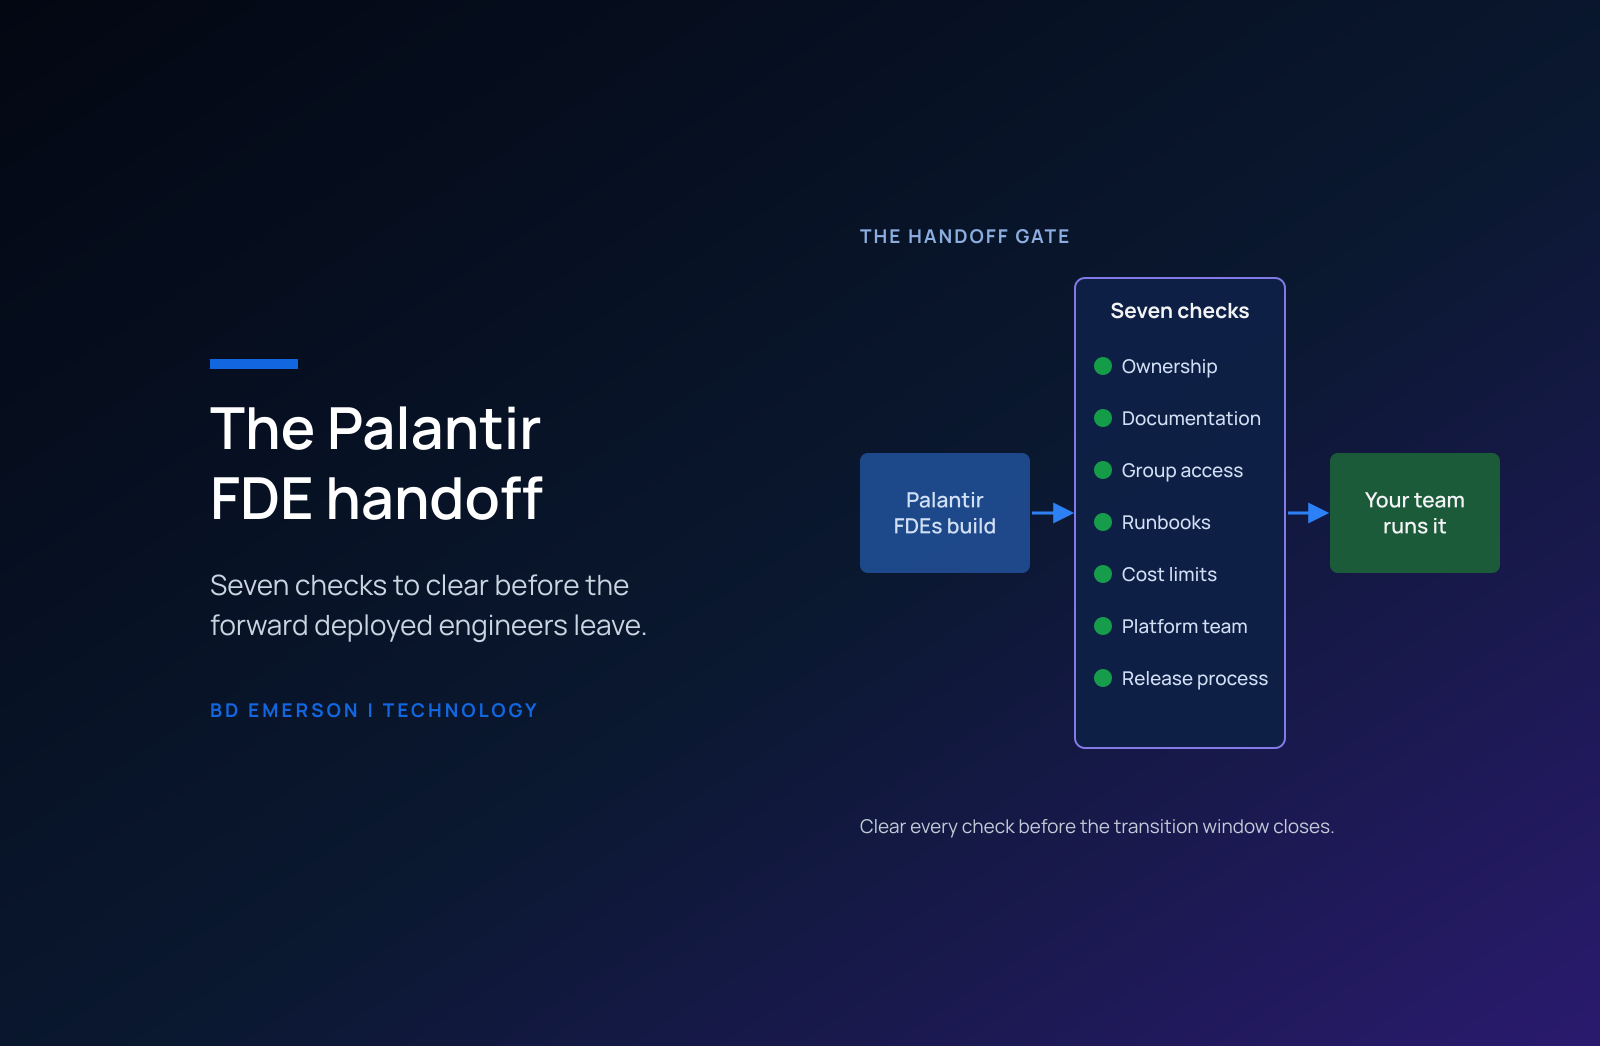
Palantir FDE Handoff: What to Have in Hand Before the Forward Deployed Engineers Leave
Read
Technology
/
November 7, 2026
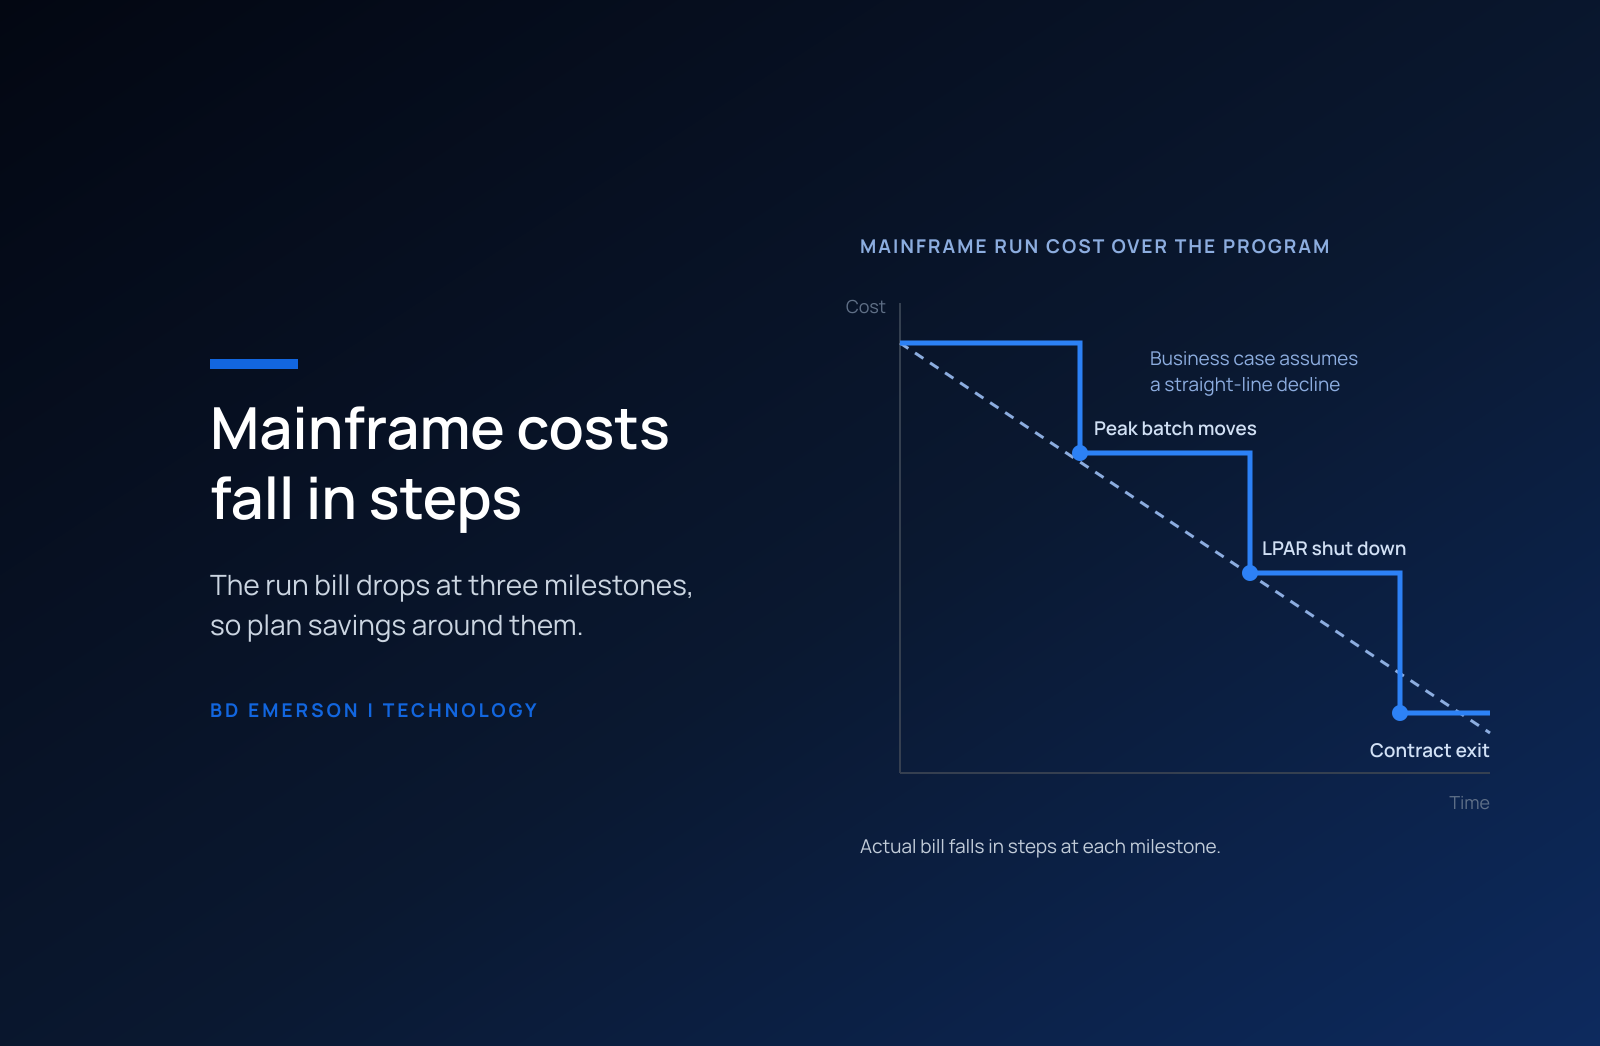
Mainframe Modernization: Five Paths, the Cost Math, and Why Programs Run Long
Read
M&A
/
November 7, 2026
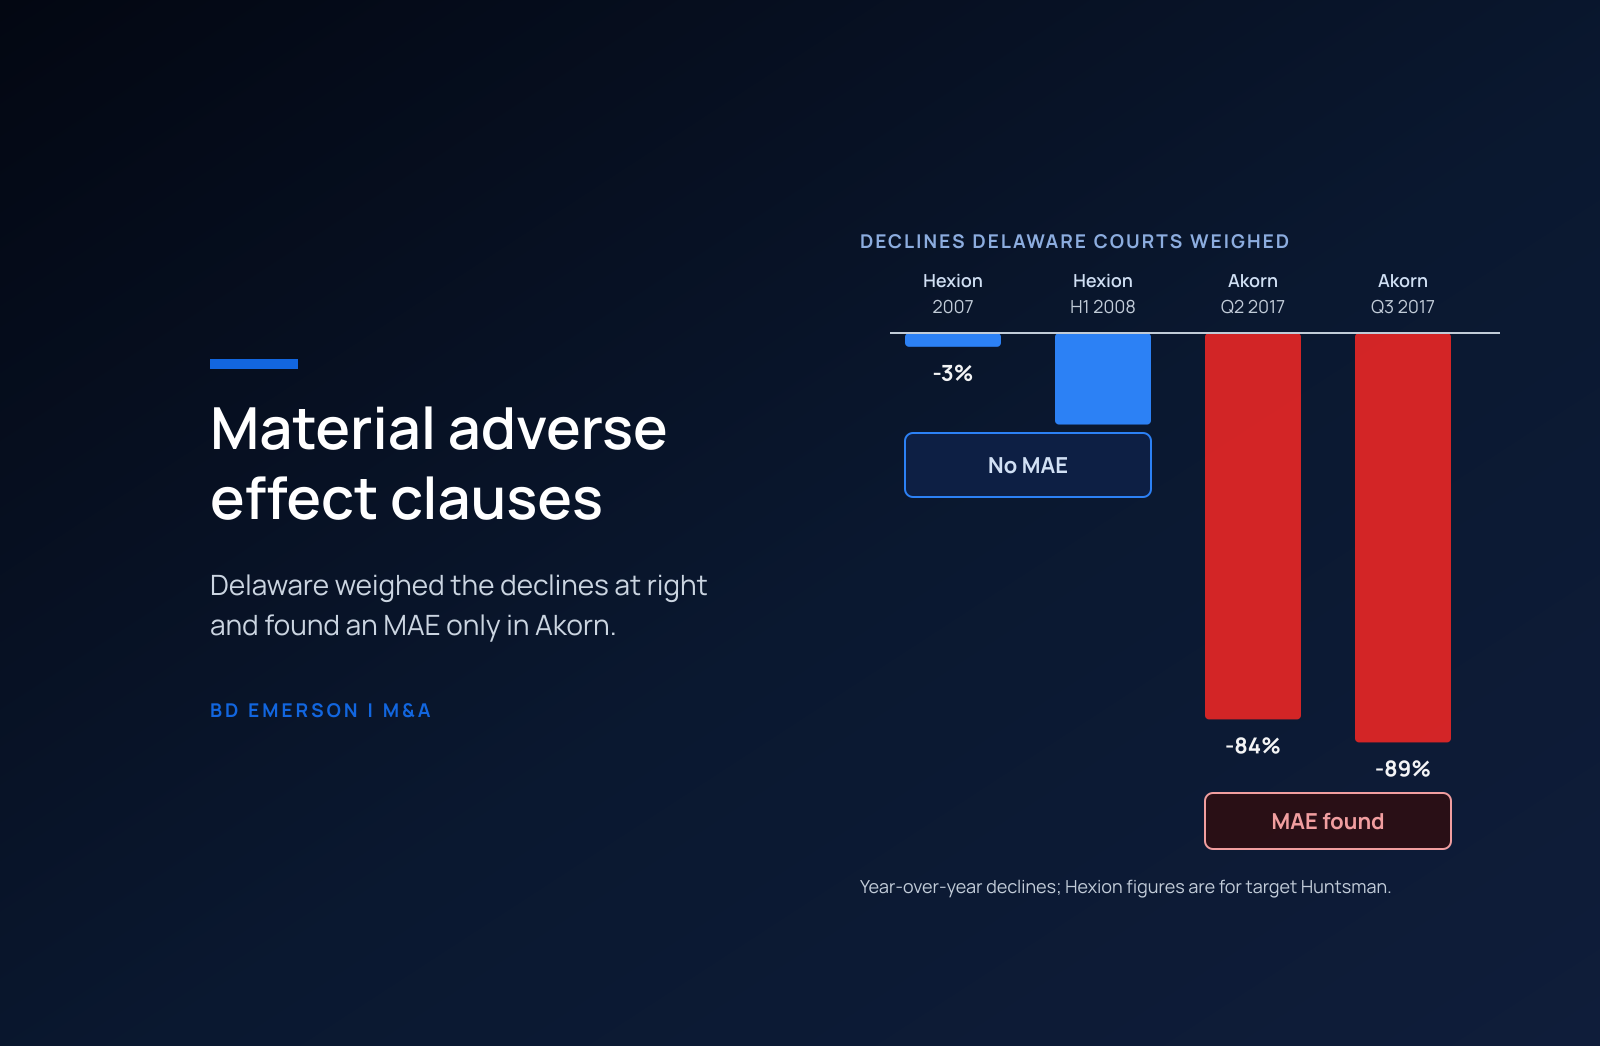
Material Adverse Effect (MAE) Clauses: What Delaware Courts Require and What the Numbers Must Show
Read
Technology
/
November 7, 2026
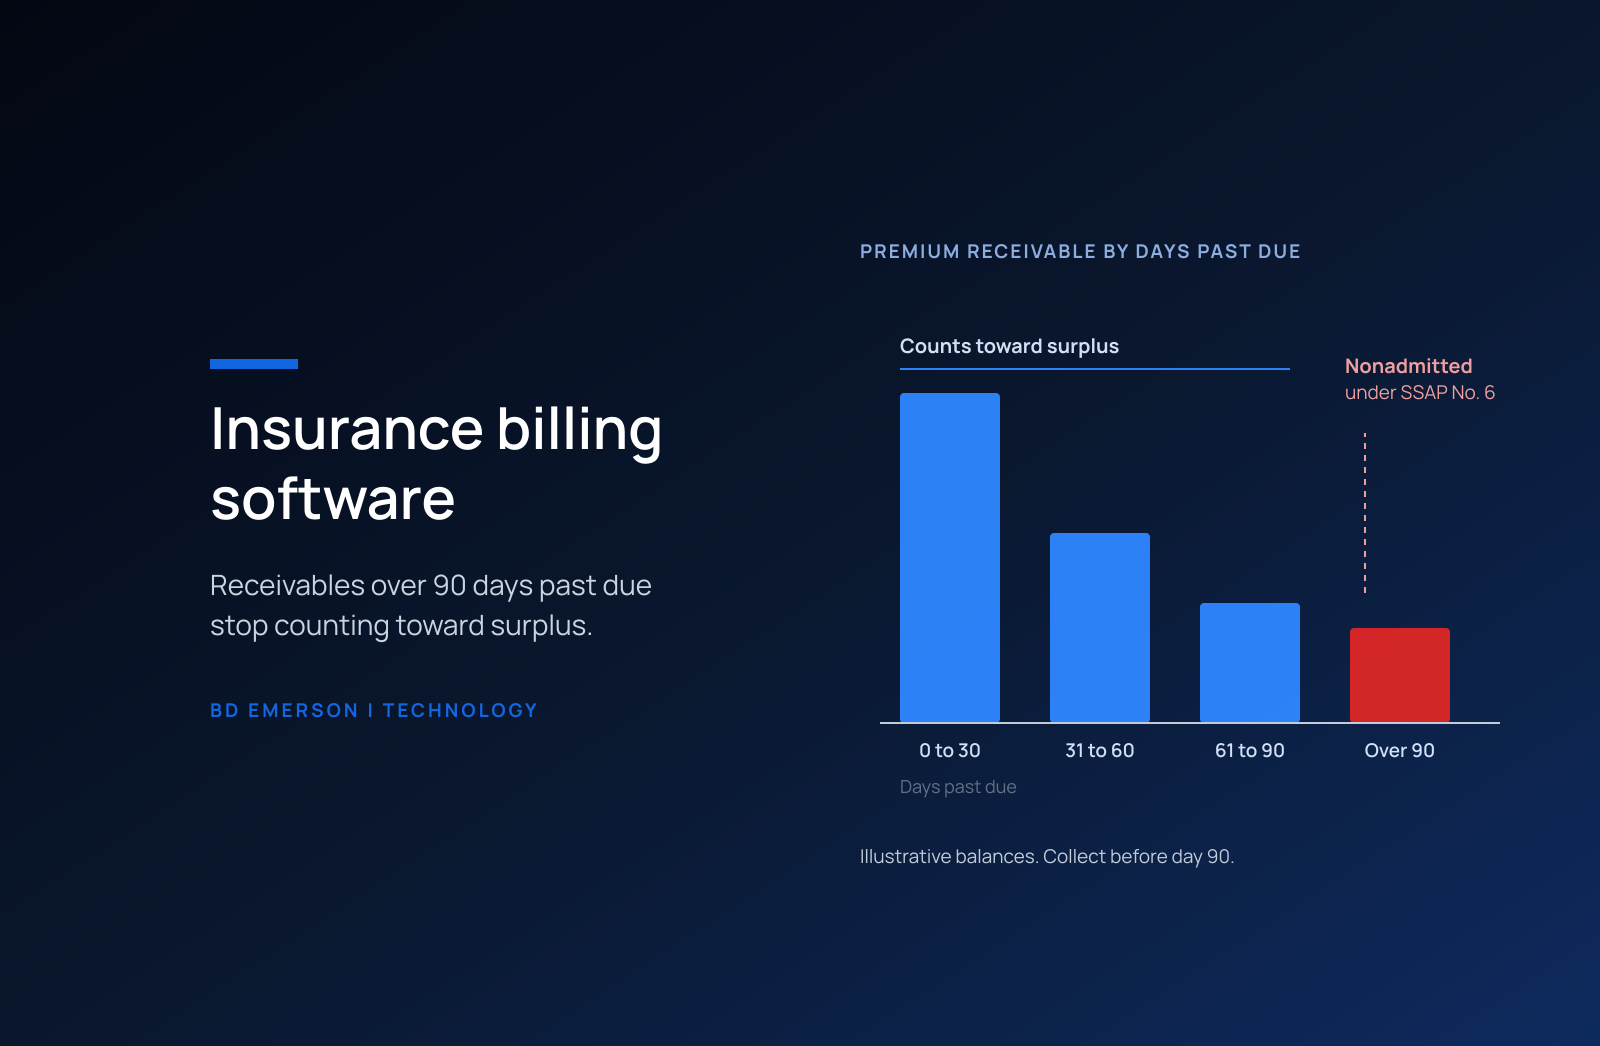
Insurance Billing Software for P&C Carriers and MGAs: What It Must Do
Read
Load More
Contact
Tell us
about your challenge.
We'll get back to you within one business day.
Fill out the form or
Book a Call
Name
*
Company
*
Business Email Address
*
Phone
Message
*
Request a quote
Thank you!
Your submission has been received!
Successfully sent
Oops! Something went wrong while submitting the form.
+1 (804) 913-3012
info@bdemerson.com
linkedin
Our Work
Home
All Services
All Industries
Case Studies
Company
About
Blog
Careers
Trust Center
Contact
©
2025
BD Emerson Website made by
Foursets
Privacy Policy
Terms and Conditions