
When a semiconductor company with several thousand employees was carved out of its parent, its security belonged to the parent. Endpoint protection, monitoring, policies, and the compliance program its defense customers depended on all ran through the parent under a transition services agreement with an end date. The new company had two security staff. It needed a full program of its own, an infrastructure move out of the parent's environment, and continuous compliance for defense and export-controlled work through the transition.
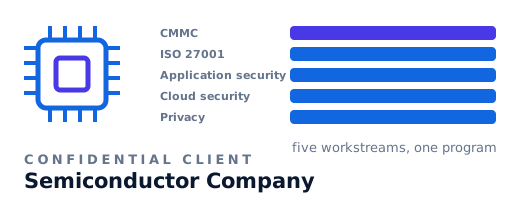
The program runs five workstreams. CMMC covers the defense business. An ISO 27001 information security management system covers the company as a whole. Application security brings testing into the development pipeline. Cloud security covers the AWS environment the company is building to leave the parent's infrastructure, along with an assessment of its Oracle Cloud estate. A privacy program covers data inventory and data subject requests, including the employee privacy obligations that come with operations in Europe. Under all five, the team is replacing the parent's day-to-day security services with the company's own endpoint management and EDR, a SIEM, a policy set written for the new company, and a network review, with compliance tracked in Vanta.
A single program office coordinates all five workstreams with the company's technology leadership, and the delivery team has grown to 17 people as the scope expanded. CMMC moved first, and the company affirmed CMMC Level 1 about four months after the program started. The ISO 27001 management system is heading to its Stage 1 audit with an accredited certification body. BD Emerson prepares companies for these assessments and does not perform them: CMMC Level 2 certification comes from an independent C3PAO, and ISO 27001 certification comes from an accredited registrar.
Seven months in, the company has CMMC Level 1 affirmed for its defense business, completed security assessments of its applications and its Oracle Cloud estate, and an ISO 27001 management system heading into audit. The rest of the program, including the cloud build and the move off the parent's infrastructure, continues on the same plan, with each workstream reporting into one program office.
Client details in this case study are generalized, and in places combined across engagements, to protect confidentiality. The program combines our carve-out advisory and cybersecurity transformation work, and our guides to IT carve-outs and TSA exit planning cover the separation side. We are glad to walk through comparable work under NDA.