
A software company had won its first federal customers through small purchases, and the larger contracts behind them required FedRAMP. The advice it had received pointed to a legacy Rev 5 assessment against the Moderate baseline, priced well above what leadership had planned to spend. The FedRAMP Consolidated Rules for 2026 had just taken effect, and the company needed to know which route would put its platform in front of agencies, at what cost, and on what timeline.
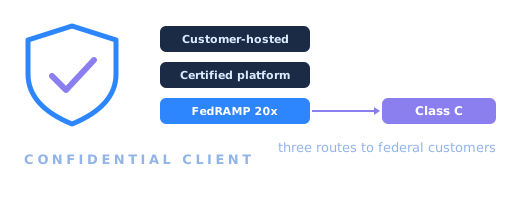
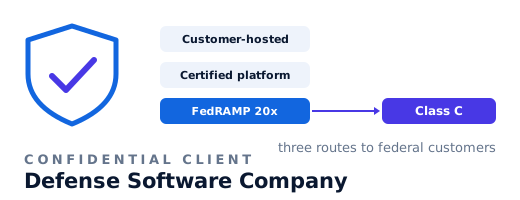
We laid out three ways to reach federal customers. The first was to ship the software for each customer to run in its own government-hosted environment, which keeps the company's cloud out of FedRAMP scope but puts deployment, updates, and support on every customer. The second was to run inside a platform provider's FedRAMP certified environment, which shortens the path but adds a recurring platform cost and ties the product's federal roadmap to the provider's. The third was to certify the company's own offering directly through FedRAMP 20x. We compared the three on cost, on time to the first federal contract, and on what each would let the company promise its customers.
Direct certification through 20x came out ahead on cost and on control of the product. FedRAMP points cloud services built on certified infrastructure to 20x, and every 20x certification comes directly from FedRAMP without an agency sponsor. We estimated the legacy Rev 5 route at roughly three times the cost, and FedRAMP stops accepting new Rev 5 applications on June 11, 2027. We recommended Class C, which FedRAMP describes as covering most Low and Moderate impact systems and which requires all 46 Key Security Indicators. Class A builds on a recent SOC 2 Type II or comparable assessment plus only 7 indicators, but FedRAMP scopes it to pilots, testing, and negligible-risk data, so it would not carry the contracts in the pipeline.
The commercial product ran in a standard public cloud region and could stay there. We designed a segregated enclave in a government cloud region: a cloned deployment for federal customers, hardened containers, and continuous monitoring built in from the start. The commercial product keeps its release pace, and only the enclave carries the federal obligations.
Class C sets the engineering bar. Each indicator needs at least two automated methods that verify and validate it, and a service already in use must supply at least six months of historical KSI metrics. The plan puts six months of monitored indicators first, followed by six to eight weeks for the independent assessment, which has to be completed within the three months before the company applies. That puts an application about eight months after monitoring starts, and every engineering task in the plan traces back to that date.
Leadership has a route, a class, and a date it can defend to its board and investors, along with the enclave design and an engineering plan built around the indicators. We introduced the company to independent FedRAMP Recognized assessors. BD Emerson prepares companies for FedRAMP and does not perform the assessment, which keeps the firm preparing you separate from the firm evaluating you.
Client details in this case study are generalized, and in places combined across engagements, to protect confidentiality. This work runs through our FedRAMP 20x readiness and FedRAMP compliance consulting practices, and our FedRAMP 20x guide covers the Key Security Indicators, the classes, and what changed from Rev 5. We are glad to walk through comparable work under NDA.