
An enterprise SaaS provider found files encrypted across its virtualization hosts. The attackers were Akira ransomware affiliates, and they had come in through a known-exploited vulnerability in an internet-facing SonicWall firewall, a route Akira affiliates have used against many companies. The provider's customers were large enterprises with their own security teams and their own questions, and breach counsel, the cyber insurer, and a forensics firm all needed to be engaged within hours.
The response ran under a privileged structure directed by breach counsel, with BD Emerson as technical lead alongside an independent forensics firm and communications kept on segregated channels. We deployed EDR across the infrastructure to see and stop what the attacker still had, rotated credentials and tokens, hunted for indicators of compromise in the identity platform, preserved logs for the forensic record, and removed the legacy authentication paths that would have let the attacker back in.
Enterprise customers wanted answers before the investigation could give them. We drafted the technical talking points the company used with its largest customers, accurate on what was known, clear about what was still under investigation, and aligned with counsel before anything went out.
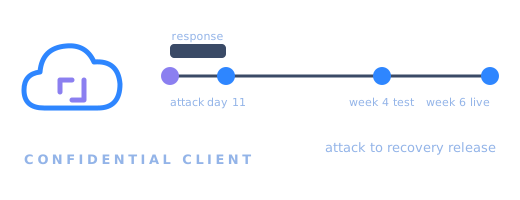
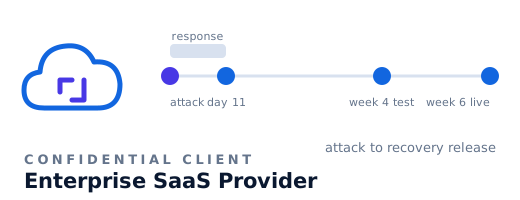
Active response ran about eleven days. The company tested its recovery release about four weeks after the attack and put it into production about six weeks after. The relationship continued after the incident: the company kept BD Emerson for managed security, its SOC 2 and ISO 27001 programs, and privacy work. The firewall flaw that let the attackers in is now one of the first things we test for, and it has turned up again in at least one sell-side penetration test since.
Client details in this case study are generalized, and in places combined across engagements, to protect confidentiality. The response ran through our cyber incident response practice. An incident response retainer puts the same team and the counsel coordination in place before an attack, and tabletop exercises rehearse the decisions while nothing is on fire. Our guide to cyber insurance requirements covers what carriers now expect. We are glad to walk through comparable work under NDA.