FedRAMP 20x Readiness & KSI Engineering
Readiness for FedRAMP 20x Class A, B, and C: profile, scope, automated KSI validations, and the JSON package FedRAMP reviews.



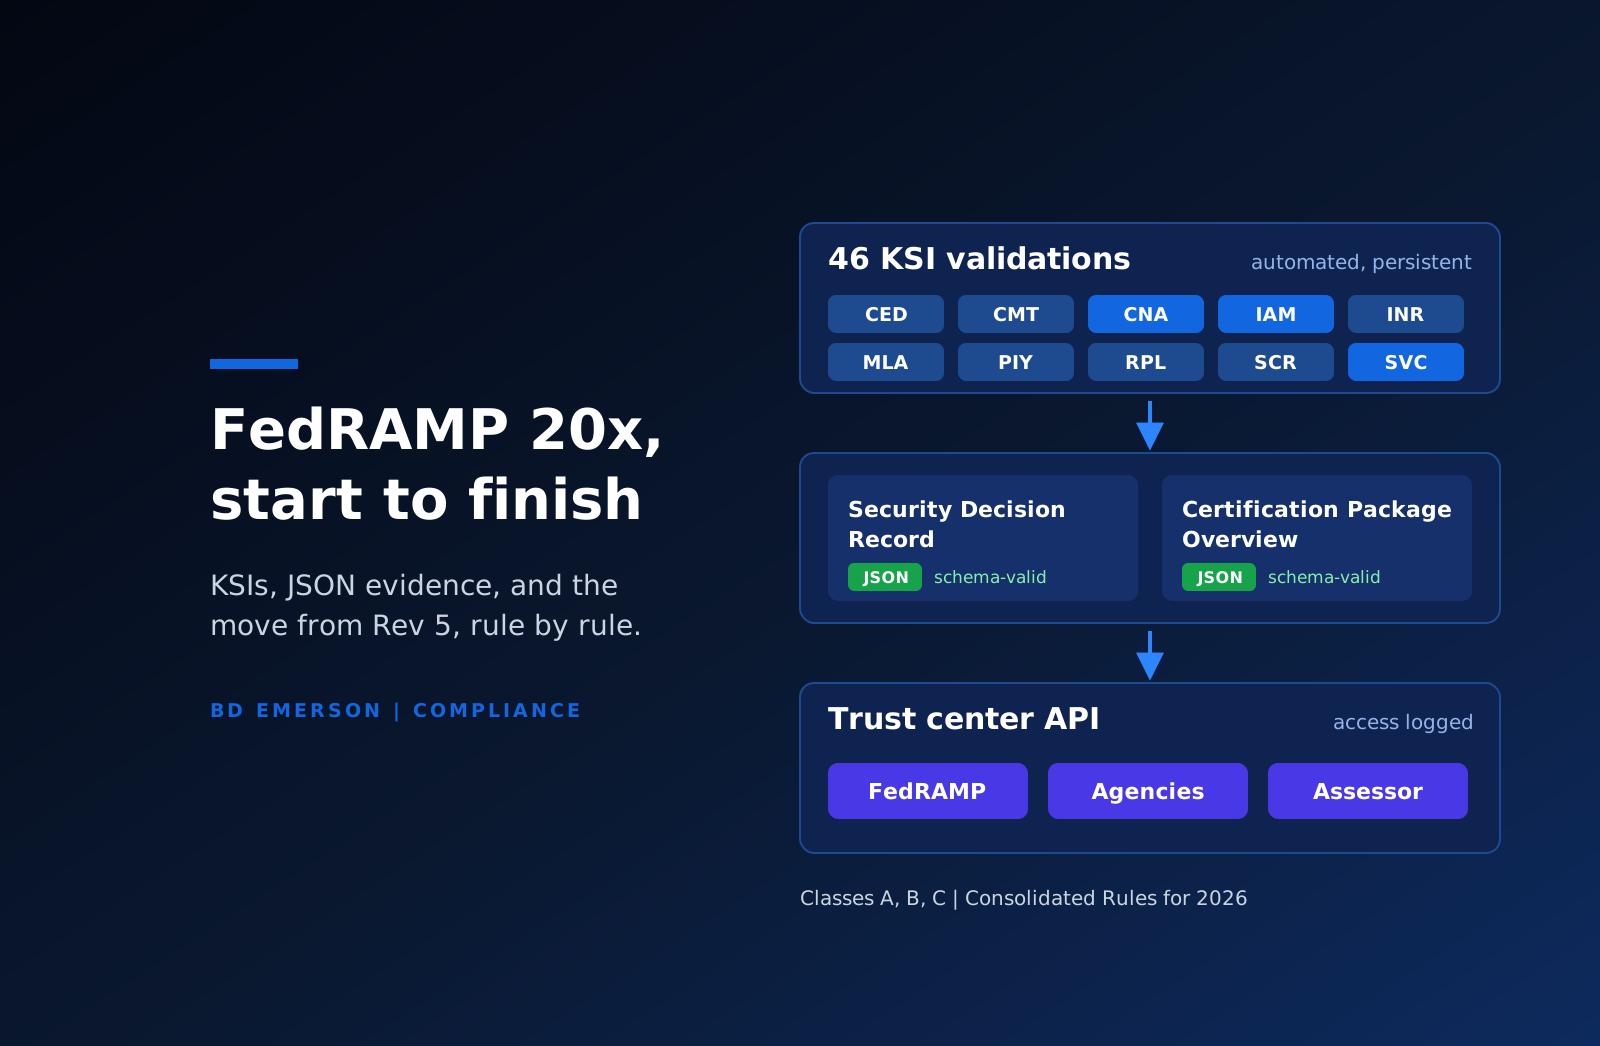
FedRAMP 20x readiness is the work a cloud service provider does before applying for a FedRAMP 20x Certification under the Consolidated Rules for 2026. It covers choosing a certification profile, drawing the Minimum Assessment Scope, designing measures for the Key Security Indicators your class requires (7 for Class A, 41 for Class B, and all 46 for Class C), automating the validations behind them, and publishing a Certification Package Overview and Security Decision Record in JSON through a FedRAMP-compatible trust center. It also covers the Ongoing Certification work, from vulnerability detection and reporting to the Ongoing Certification Report every three months, because FedRAMP expects that work to be running before it certifies a service.


We confirm that 20x fits your offering, pick the class your buyers need, and name the target profile, so every FedRAMP Practice that comes with it is in scope from the first week.
Your engineers own the measurements. We design each KSI measure with them, including its data source, cadence, and failure condition, and map every applicable rule in the Security Decision Record.
We trace each validation from source data through code and thresholds to the result, as FedRAMP tells assessors to, and fix the gaps a green status can hide.
Before you apply, the recurring work is already running: resource validation, vulnerability reporting, a current package, and a real or example Ongoing Certification Report.

We work in the formats FedRAMP reviews: JSON validated against the published schemas, rules mapped from FedRAMP's machine-readable dataset, and validations your team can rerun on demand.
We do not assess what we advise on, and we are not a FedRAMP Recognized assessor. Your team owns the program, and your assessor keeps the independence FedRAMP requires.
SOC 2 readiness for a Class A prerequisite, penetration testing for vulnerability detection, and CMMC for defense contracts sit in the same firm, so evidence carries across programs.


Great consulting firms for scaling security, compliance, and appsec.


Outstanding partner in Technical and Cyber Due Diligence

Appsec maturity and application hardening.

BD Emerson helped us simplfiy our compliance management.

BD Emerson did such a phenomenal job. What started as privacy support quickly became a full partnership across compliance, engineering, and even business operations. They’re embedded with our team. They understand our product. They move fast. They’re simply invaluable.
Great consulting firms for scaling security, compliance, and appsec.
Outstanding partner in Technical and Cyber Due Diligence
Appsec maturity and application hardening.
BD Emerson helped us simplfiy our compliance management.
BD Emerson did such a phenomenal job. What started as privacy support quickly became a full partnership across compliance, engineering, and even business operations. They’re embedded with our team. They understand our product. They move fast. They’re simply invaluable.

We had a hard time finding the right company to partner with in support of our compliance journey. Some vendors sell the idea that they do the work, but then you end up doing everything. The ambiguity is what killed our last project. BD Emerson’s team has such great technical knowledge and understands the standard so well that they made us comfortable with moving fast. This has led to us closing major enterprise customers that were previously out of reach because of security and compliance.

Lead an enterprise initiative to overhaul the organization's technology stack from ecommerce, corporate tech, and corporate security.

Supported ISO 42001 exercise and served as internal auditor.

Rubrik's privacy and compliance team began with the backbone of BD Emerson. BD Emerson supported building out the privacy program, GRC (ISO 27001, SOC 2, CMMC, FedRAMP), and the appsec function.

We needed a partner who could move quickly, without sacrificing precision. BD Emerson brought the expertise, structure, and speed we were looking for. Their team became an extension of ours, embedding themselves across the organization, guiding us step by step, and giving us confidence in areas we hadn’t tackled before. The internal audit they conducted was so detailed that even the external auditors called it out. Achieving ISO 27001 with zero nonconformities says everything you need to know about the quality of the partnership.
We had a hard time finding the right company to partner with in support of our compliance journey. Some vendors sell the idea that they do the work, but then you end up doing everything. The ambiguity is what killed our last project. BD Emerson’s team has such great technical knowledge and understands the standard so well that they made us comfortable with moving fast. This has led to us closing major enterprise customers that were previously out of reach because of security and compliance.
Lead an enterprise initiative to overhaul the organization's technology stack from ecommerce, corporate tech, and corporate security.
Supported ISO 42001 exercise and served as internal auditor.
Rubrik's privacy and compliance team began with the backbone of BD Emerson. BD Emerson supported building out the privacy program, GRC (ISO 27001, SOC 2, CMMC, FedRAMP), and the appsec function.
We needed a partner who could move quickly, without sacrificing precision. BD Emerson brought the expertise, structure, and speed we were looking for. Their team became an extension of ours, embedding themselves across the organization, guiding us step by step, and giving us confidence in areas we hadn’t tackled before. The internal audit they conducted was so detailed that even the external auditors called it out. Achieving ISO 27001 with zero nonconformities says everything you need to know about the quality of the partnership.

BD Emerson didn’t just help us meet our compliance goals; they integrated security and privacy into the core of our operations. I highly recommend BD Emerson to anyone seeking SOC 2 or GDPR compliance, or simply looking to enhance their security team and boost customer trust in their product and services. Their dedication and expertise have been invaluable to our success.


BD Emerson understood our business requirements and worked side-by-side with us. The policies and controls we developed together not only meet compliance standards but improve how we operate day to day.

From day one, BD Emerson brought urgency, clarity, and a sharp understanding of what truly matters to our business — earning and keeping customer trust. They went beyond helping us meet compliance requirements; they helped build a foundation for secure, scalable growth. That kind of partnership is rare.

BD Emerson didn’t just help us pass an audit—they helped us build a sustainable culture of security.

BD Emerson was essential in helping our company navigate the daunting process of leveling up our security infrastructure. BD Emerson’s impressive expertise and confidence throughout the process helped our team exceed HIPAA and SOC 2 Type 1 standards quickly, distilling what can be an overwhelming process into a streamlined, organized effort. From day one they began adding value and getting us on course. With their help we delivered on a massive security overhaul with both extreme efficiency and thorough attention to details. Because of BD Emerson’s support, we’ve increased our clients’ trust in Titan Intake and the life-changing work it accomplishes for those seeking specialist referrals.

BD Emerson didn’t just help us meet our compliance goals; they integrated security and privacy into the core of our operations. I highly recommend BD Emerson to anyone seeking SOC 2 or GDPR compliance, or simply looking to enhance their security team and boost customer trust in their product and services. Their dedication and expertise have been invaluable to our success.
BD Emerson understood our business requirements and worked side-by-side with us. The policies and controls we developed together not only meet compliance standards but improve how we operate day to day.
From day one, BD Emerson brought urgency, clarity, and a sharp understanding of what truly matters to our business — earning and keeping customer trust. They went beyond helping us meet compliance requirements; they helped build a foundation for secure, scalable growth. That kind of partnership is rare.
BD Emerson didn’t just help us pass an audit—they helped us build a sustainable culture of security.
BD Emerson was essential in helping our company navigate the daunting process of leveling up our security infrastructure. BD Emerson’s impressive expertise and confidence throughout the process helped our team exceed HIPAA and SOC 2 Type 1 standards quickly, distilling what can be an overwhelming process into a streamlined, organized effort. From day one they began adding value and getting us on course. With their help we delivered on a massive security overhaul with both extreme efficiency and thorough attention to details. Because of BD Emerson’s support, we’ve increased our clients’ trust in Titan Intake and the life-changing work it accomplishes for those seeking specialist referrals.