ESPR Compliance and Digital Product Passports


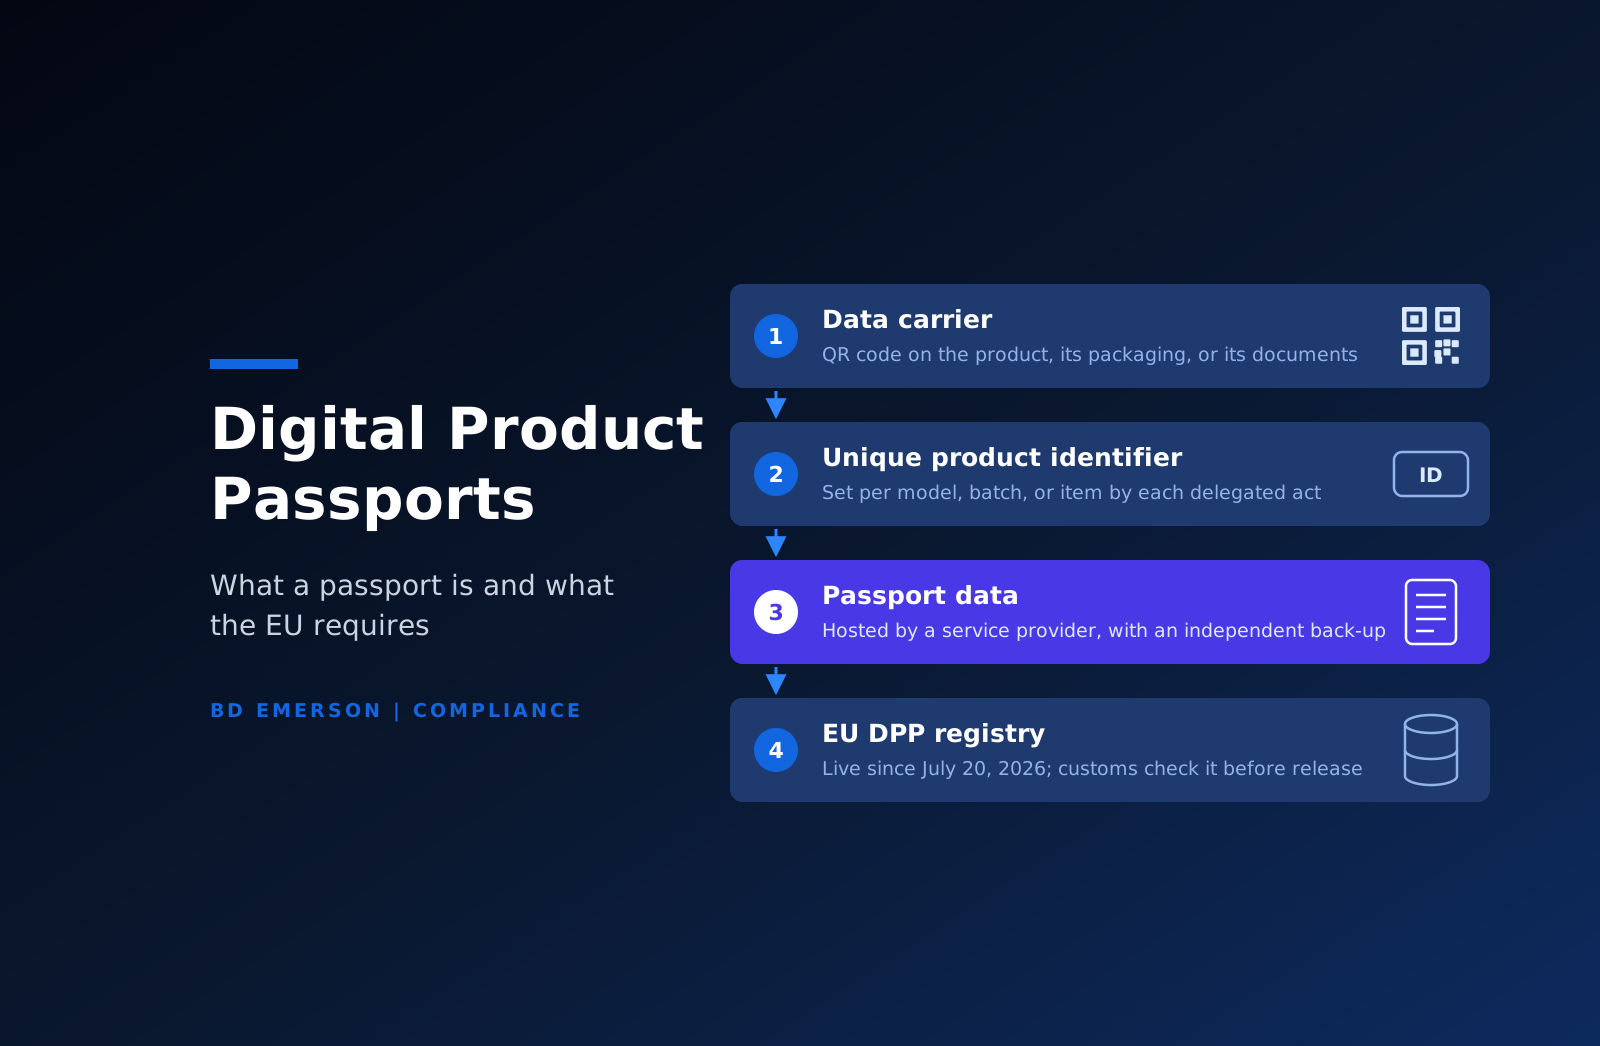
ESPR compliance means meeting Regulation (EU) 2024/1781, the Ecodesign for Sustainable Products Regulation, in force since July 18, 2024 and covering almost every physical product placed on the EU market, wherever it is made. Some duties already apply: since July 19, 2026, large companies may not destroy unsold apparel, clothing accessories, or footwear, and large companies that discard unsold consumer products must disclose it each year. Product rules arrive through delegated acts that apply at least 18 months after they enter into force, and each act can require a digital product passport registered in the EU registry that went live on July 20, 2026. The Commission's schedule starts with iron and steel and continues through textiles, tires, aluminum, furniture, and mattresses.
Your product list, sourcing countries, and EU sales channels go into one register that shows each product group, your role, and every obligation with its date.
The destruction ban and the unsold goods disclosure apply before any product-specific act, and older ecodesign measures still cover many energy-related products. We close those first.
Data model, supplier collection, platform selection, and integration run against the delegated act for your product group, timed so passports are ready before the act applies.
We register identifiers before products reach the market, track new delegated acts and standards, and update data requirements when the rules change.

Send us your EU product list and sales channels. We will show you which obligations apply today, what the Commission has scheduled for your product groups, and the data your passports need.

ESPR requires passport data to be authenticated, reliable, and secure, with different access for customers, repairers, recyclers, and authorities. Our practice runs SOC 2, ISO 27001, and privacy programs, so access control, integrity, and audit trails go into the design from the first workshop.

We do not sell or resell a passport platform. We write the requirements from the delegated act and the EN standards, run the selection, and integrate the platform you choose, so the recommendation follows your products and your systems.

BD Emerson is joining Andersen Consulting, announced August 10, 2026, with closing expected in Q4 2026. Andersen Global's member and collaborating firms operate in 170 countries, so the legal and tax questions an ESPR program raises in EU member states can go to Andersen colleagues.
Great consulting firms for scaling security, compliance, and appsec.
Outstanding partner in Technical and Cyber Due Diligence
Appsec maturity and application hardening.
BD Emerson helped us simplfiy our compliance management.
BD Emerson did such a phenomenal job. What started as privacy support quickly became a full partnership across compliance, engineering, and even business operations. They’re embedded with our team. They understand our product. They move fast. They’re simply invaluable.
We had a hard time finding the right company to partner with in support of our compliance journey. Some vendors sell the idea that they do the work, but then you end up doing everything. The ambiguity is what killed our last project. BD Emerson’s team has such great technical knowledge and understands the standard so well that they made us comfortable with moving fast. This has led to us closing major enterprise customers that were previously out of reach because of security and compliance.
Lead an enterprise initiative to overhaul the organization's technology stack from ecommerce, corporate tech, and corporate security.
Supported ISO 42001 exercise and served as internal auditor.
Rubrik's privacy and compliance team began with the backbone of BD Emerson. BD Emerson supported building out the privacy program, GRC (ISO 27001, SOC 2, CMMC, FedRAMP), and the appsec function.
We needed a partner who could move quickly, without sacrificing precision. BD Emerson brought the expertise, structure, and speed we were looking for. Their team became an extension of ours, embedding themselves across the organization, guiding us step by step, and giving us confidence in areas we hadn’t tackled before. The internal audit they conducted was so detailed that even the external auditors called it out. Achieving ISO 27001 with zero nonconformities says everything you need to know about the quality of the partnership.
BD Emerson didn’t just help us meet our compliance goals; they integrated security and privacy into the core of our operations. I highly recommend BD Emerson to anyone seeking SOC 2 or GDPR compliance, or simply looking to enhance their security team and boost customer trust in their product and services. Their dedication and expertise have been invaluable to our success.
BD Emerson understood our business requirements and worked side-by-side with us. The policies and controls we developed together not only meet compliance standards but improve how we operate day to day.
From day one, BD Emerson brought urgency, clarity, and a sharp understanding of what truly matters to our business — earning and keeping customer trust. They went beyond helping us meet compliance requirements; they helped build a foundation for secure, scalable growth. That kind of partnership is rare.
BD Emerson didn’t just help us pass an audit—they helped us build a sustainable culture of security.
BD Emerson was essential in helping our company navigate the daunting process of leveling up our security infrastructure. BD Emerson’s impressive expertise and confidence throughout the process helped our team exceed HIPAA and SOC 2 Type 1 standards quickly, distilling what can be an overwhelming process into a streamlined, organized effort. From day one they began adding value and getting us on course. With their help we delivered on a massive security overhaul with both extreme efficiency and thorough attention to details. Because of BD Emerson’s support, we’ve increased our clients’ trust in Titan Intake and the life-changing work it accomplishes for those seeking specialist referrals.